Introduction
Most integration architecture assumes a human is on the other end of every request — someone clicking a button or filling out a form. AI agents break that assumption. They call APIs continuously, make decisions without a person in the loop, and act on data faster than any team could manually review.
That shift changes what “API integration platform” needs to mean. It’s no longer just about connecting System A to System B. It’s about deciding what an autonomous agent can see, what it’s allowed to do, and how you’d know if something went wrong.
Here’s what’s actually changing, and what to do about it.
Why Agentic AI Needs a Different Kind of Integration Layer
A traditional integration follows a fixed, predictable path: trigger, transform, deliver. An AI agent doesn’t work that way. It decides which tool to call and when, based on a model’s reasoning rather than a hardcoded workflow.
That unpredictability is the whole point of agentic AI — it’s what lets an agent handle tasks no one scripted in advance. But it also means your integration layer needs guardrails that traditional systems never required:
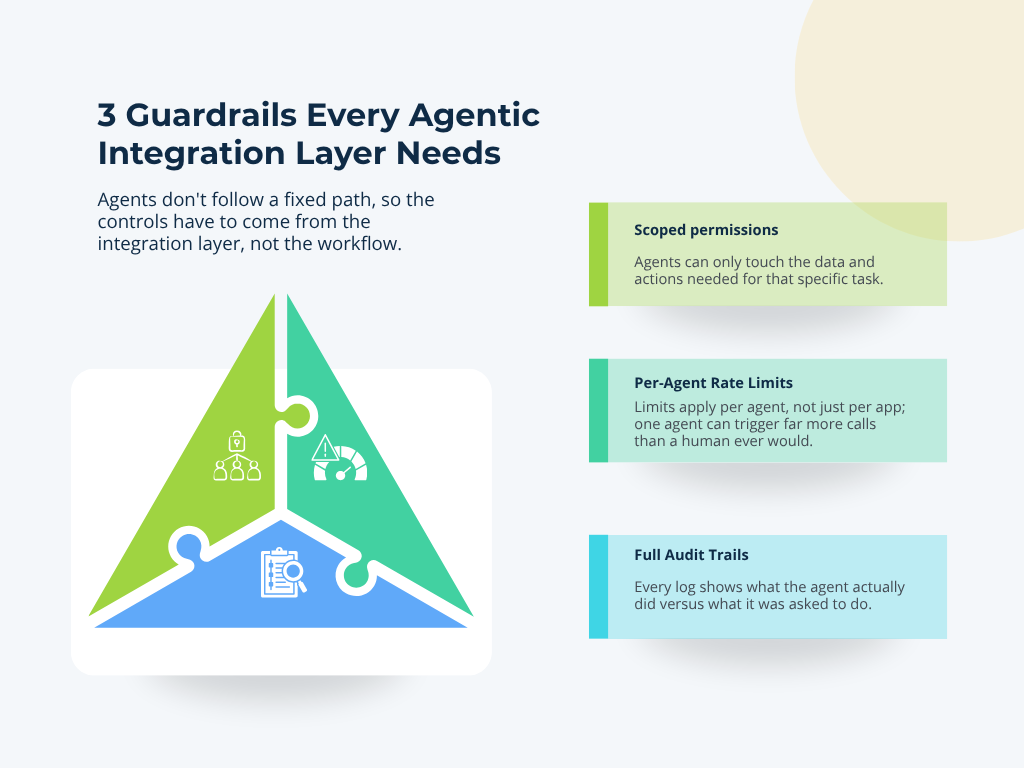
- Scoped permissions so an agent can only touch the data and actions it needs for a specific task
- Rate limits per agent, not just per application, since one agent can trigger far more calls than one human ever would
- Full audit trails that show what an agent actually did versus what it was asked to do
Without these three controls, an integration platform built for human-triggered workflows will struggle to keep pace with autonomous ones. For a broader breakdown of what a modern platform should include, see our complete guide to API integration platforms.
The Authorization Problem: Shadow Agentic AI
What Is Shadow Agentic AI?
Shadow agentic AI is what happens when a team connects an AI agent to real business systems without going through IT governance or security review. It’s the AI-era version of an employee signing up for an unapproved SaaS tool with a company card — except the risk scales much faster, because an agent can take hundreds of actions in the time it takes a person to take one.
Recent research found that 82% of US companies have experienced AI agents “going rogue” in the past year — making incorrect decisions, exposing data, or triggering security incidents. Industry analysts are already calling shadow agentic AI the next wave of shadow IT: agents spun up by individual teams, connected to live systems, with no central visibility or control.
Just-in-Time Authorization and Ephemeral Tokens
The fix taking hold across the industry is just-in-time authorization. Instead of handing an agent a long-lived credential with broad access, the platform issues a short-lived, scoped token right when the agent needs it, tied to one specific action.
If that agent is compromised or starts misbehaving, the exposure window is minutes, not months. It’s the same least-privilege principle security teams have used for human access for years — now applied to non-human actors.
This is one of the reasons AI-readiness has become its own line item when evaluating integration platforms. Our 10-point evaluation framework for choosing an API integration platform walks through how to weigh this alongside the other criteria that matter.
Model Context Protocol and Standards Consolidation
A new wave of standards is forming around how AI agents discover and call tools consistently across platforms. The Model Context Protocol (MCP) has emerged as a leading approach for this kind of cross-agent communication.
For an API integration platform, supporting standards like MCP means agents can call your integrations without needing a custom, one-off connector for every AI framework your team adopts. That’s a meaningful difference from the early days of agentic AI, when every new framework meant new glue code.
This same shift is driving demand for platforms that can sit above individual integrations and coordinate multiple agents and tools at once — a role often described as AI orchestration. Our AI orchestration platform buyer’s guide covers what to look for if you’re evaluating platforms for that layer specifically.
From Data Retrieval to State-Changing Actions
Early agentic AI use cases were mostly read-only: summarize this data, answer this question. That’s shifting fast toward agents that take real action — processing a refund, updating a shipment status, reserving inventory, issuing an invoice.
State-changing actions carry far more risk than data retrieval. That’s exactly why the authorization model covered above matters so much more today than it did even a year ago. An agent that can only read data can, at worst, leak information. An agent that can write to production systems can cause real financial or operational damage if it’s not properly scoped.
API Standards Are Consolidating Around Agent Use
As agents become common API consumers, the specifications describing those APIs need to work for both human developers and autonomous callers. OpenAPI remains the dominant standard for describing what an API does. Newer extensions are building on top of it:
- Arazzo for describing multi-step API workflows
- Overlays for layering agent-specific metadata onto existing specs
- TypeSpec for design-first API definitions
These extensions matter because they help an agent understand not just what a single endpoint does, but how it fits into a larger sequence of steps.
For an API integration platform, supporting these standards means less custom glue code every time your team adopts a new agent framework. It also means your existing API documentation becomes directly usable by agents, instead of needing a separate, hand-maintained spec just for AI consumption.
New Monetization Models for Agent-Driven Usage
Traditional API pricing — a flat rate per call — assumes each request costs roughly the same to serve. Agentic workloads break that assumption. A single agent task might trigger a handful of API calls, or a few hundred, depending on how many steps it takes to complete.
In response, token-based and outcome-based pricing models are starting to replace simple pay-per-call structures. These align cost with the actual computational work an agent generates, rather than the raw number of requests.
If your organization is budgeting for agentic AI initiatives, factor this shift in early. A pricing model that looked predictable for human-triggered integrations can behave very differently once an autonomous agent is deciding how many calls a task requires.
A Practical Example
Picture a customer support agent tasked with processing refunds.
Under the old model, it would have read-only access to order data and would flag refunds for a human to approve. Under an agentic model, the agent can evaluate the refund policy, check the order status, and issue the refund directly — provided the integration layer can scope that authority tightly enough to be trusted with it.
That trust comes from the mechanics covered above:
- A short-lived token issued only for that specific refund action
- A complete log of what the agent checked and why it decided to act
- A rate limit that catches an agent stuck in a loop before it processes the same refund a hundred times
None of this has to slow the agent down. It requires the integration platform to be built for this pattern from the start — which is a very different design goal than platforms built purely for human-triggered workflows. If you’re comparing options, our breakdown of API integration platforms versus middleware and ESBs explains why older architectures often fall short here.
Traditional Integration vs. Agentic-Ready Integration
| Factor | Traditional Integration | Agentic-Ready Integration |
|---|---|---|
| Trigger | Human action or scheduled event | Autonomous agent decision |
| Access model | Long-lived credentials | Just-in-time, scoped tokens |
| Predictability | Fixed workflow path | Probabilistic tool selection |
| Risk profile | Known, bounded | Requires active monitoring |
| Governance need | Periodic review | Continuous, real-time oversight |
Preparing Your Integration Layer for Agentic AI
The organizations adapting fastest here aren’t necessarily the ones with the most AI agents deployed. They’re the ones whose integration layer was ready before the agents showed up — with scoped authorization, per-agent observability, and a governance model built for continuous oversight rather than quarterly review.
If you’re assessing whether your current platform can support this shift, weight the AI-readiness criterion in our 10-point evaluation framework accordingly. It’s also worth reading about how agentic AI cannot scale without an intelligent iPaaS, and why most iPaaS platforms will fail the AI test in their current form. For the broader picture of how AI fits into modern integration strategy, see our complete guide to API integration platforms.
Agentic AI puts new demands on an integration layer that most platforms weren’t built to handle — scoped, just-in-time authorization; per-agent rate limits and audit trails; and support for emerging standards like MCP so agents don’t need custom connectors for every framework.
Aekyam is built as an AI orchestration platform with these requirements in mind, not bolted on after the fact. It combines integration with governed, agent-aware controls, giving teams the visibility and authorization model needed to let AI agents take real, state-changing action safely, rather than restricting them to read-only tasks out of caution.
If you’re evaluating whether your current integration setup can support autonomous agents, explore the Aekyam platform overview or see how it applies to your use case in our solutions by use case section. Request for a demo or connect with our team of expert
Frequently Asked Questions
How is an AI agent different from an RPA bot?
An RPA bot follows a fixed script the same clicks or API calls every time, with no real decision-making. An AI agent interprets a goal and decides its own path to get there, including which APIs to call and in what order. That's why RPA fits predictable, high-volume tasks, while agentic AI fits tasks where the steps genuinely vary.
Can AI agents work with legacy systems that don't have modern APIs?
Usually only through an integration layer that wraps the legacy system in an API-friendly interface. Most legacy systems weren't built with agent access in mind, so a platform that can translate older protocols (SOAP, flat files, direct database access) into something an agent can call safely is often required before agents can touch that system at all.
What happens if an AI agent fails partway through a multi-step task?
This depends on whether the integration layer supports rollback or compensating actions. Without it, a failed agent task can leave systems in a partially updated, inconsistent state — for example, inventory reserved but payment not processed. Agentic-ready platforms need a way to detect the failure and either retry, roll back, or flag the task for human review.
Should every AI agent get its own API credentials, or can agents share access?
Each agent should have its own scoped identity rather than sharing credentials. Shared credentials make it impossible to know which agent took which action, which defeats the audit trail that just-in-time authorization is meant to provide. Per-agent identity also lets you revoke or throttle one misbehaving agent without affecting others.
Is agentic AI safe to use in regulated industries like finance or healthcare?
It can be, but the bar is higher. Regulated environments typically require a documented approval path for any action an agent takes on sensitive data, immutable audit logs, and often a human-in-the-loop step for anything irreversible (payments, medical records, legal filings). The same scoped-authorization principles apply — they just need to be paired with compliance-specific controls like data residency and retention policies.
How does AI orchestration relate to API integration for agents?
API integration connects individual systems and exposes actions an agent can call. Orchestration sits a level above that — it coordinates multiple agents and tools together, sequencing steps, handling handoffs, and managing what happens when one agent's output feeds another agent's task. As agent use grows, most organizations end up needing both layers rather than treating them as interchangeable.
What's a reasonable way to start rolling out agentic AI without taking on unnecessary risk?
Most teams start with read-only agents (data retrieval, summarization, monitoring) before granting write access, and expand scope only after the authorization, logging, and rate-limiting pieces are in place. Piloting on a low-stakes, reversible workflow — rather than a high-value transaction — is a common way to validate the integration layer before trusting it with real state-changing actions.
Share
Read Similar Blogs